Evaluating Geordie AI?
Try Autonomous in your environment.
See which AI agents your employees use, what they access and which threats Autonomous blocks on the endpoint. Our engineers set up your evaluation in your own environment.
- 5M AI agents protected
- SOC 2 Type II
- SSO, SCIM & SIEM
What to check in an AI agent security platform.
Compare coverage, deployment, enforcement and time to value in your own environment.
- 01
Coverage
Full visibility into 60+ supported AI applications, including Claude, Cursor, Codex Desktop, ChatGPT, Antigravity and Opencode. Each with its models, MCP servers, skills and credentials.
- 02
Deployment
An endpoint agent for macOS, Windows, Linux and containers, in the cloud too, deployed manually or through your MDM. A browser extension and SaaS integrations. A 10-minute integration.
- 03
Monitoring
Track prompts, tool calls, commands and data access. Monitor AI activity in real time.
- 04
Enforcement
Govern each agent, MCP server and skill as approved, restricted or prohibited. Stop risky agent behavior and data leaks inline with guardrails and deterministic DLP.
- 05
Data handling
You configure what is collected and for how long, 60 days at most. Stored in AWS US data centers by default. Never used to train models. SOC 2 Type II. Security policy
- 06
The trial
7 days, full access. Set up by our engineers in your own environment. You leave with an inventory of your AI agents, risk findings and tested policies. No credit card.


Trusted by security teams protecting 5M AI agents

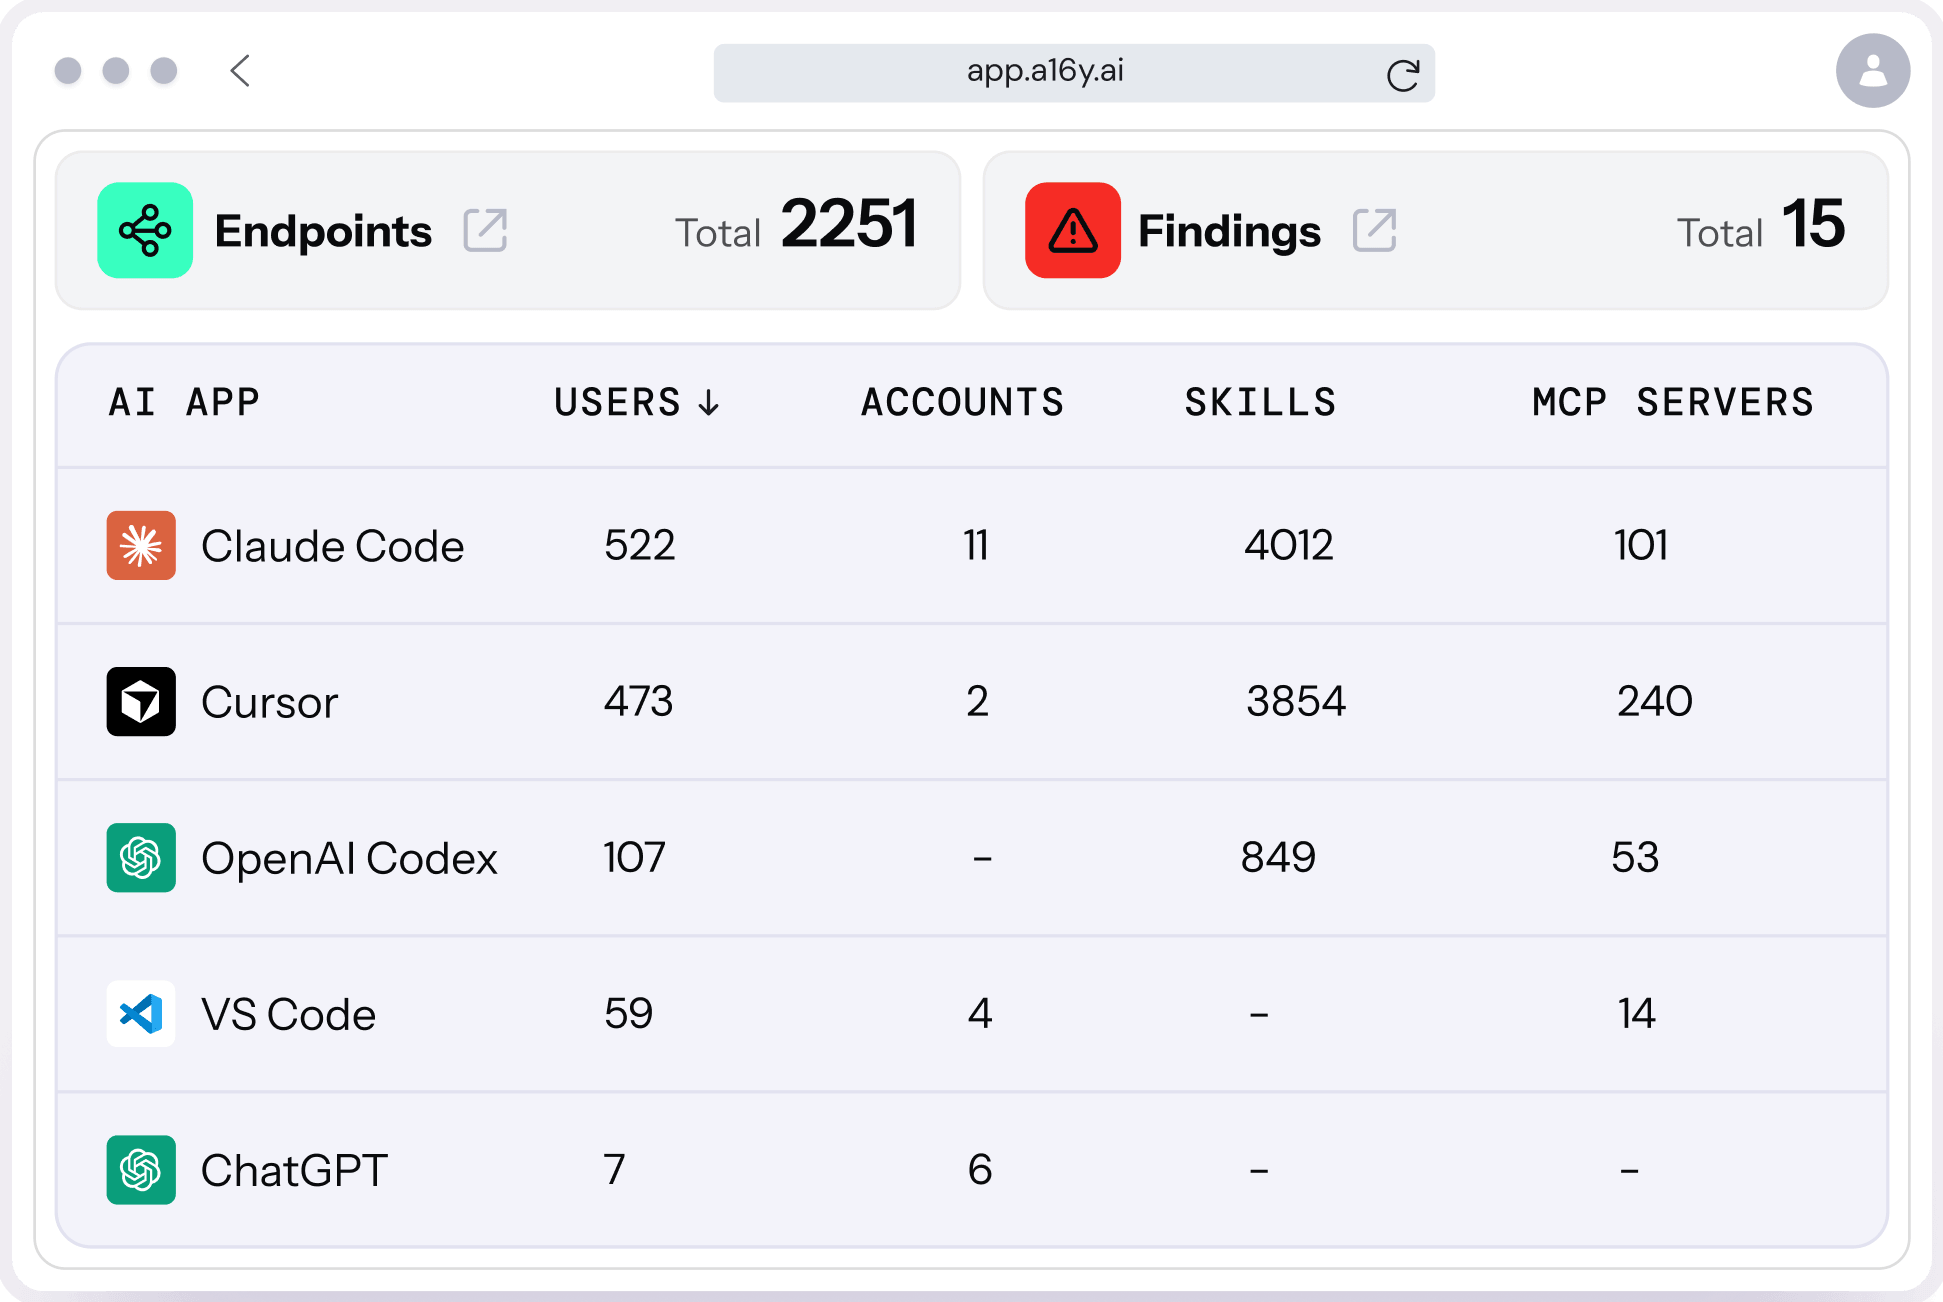
See which AI agents, accounts, skills and MCP servers are in use.
What is Autonomous?
One platform for AI agent security, governance and monitoring across the organization.
It inventories AI use, shadow AI included, from agents, MCP servers and skills to models, accounts and the credentials they hold, through native endpoint and browser agents. It scores every MCP server, skill and AI app for risk, enforces what is approved, restricted or prohibited, and stops unsafe actions inline with AI guardrails and deterministic DLP. It secures over 60 of the most popular AI agents, from the endpoint to the browser and SaaS.
- SSO / SCIM
- SIEM integration
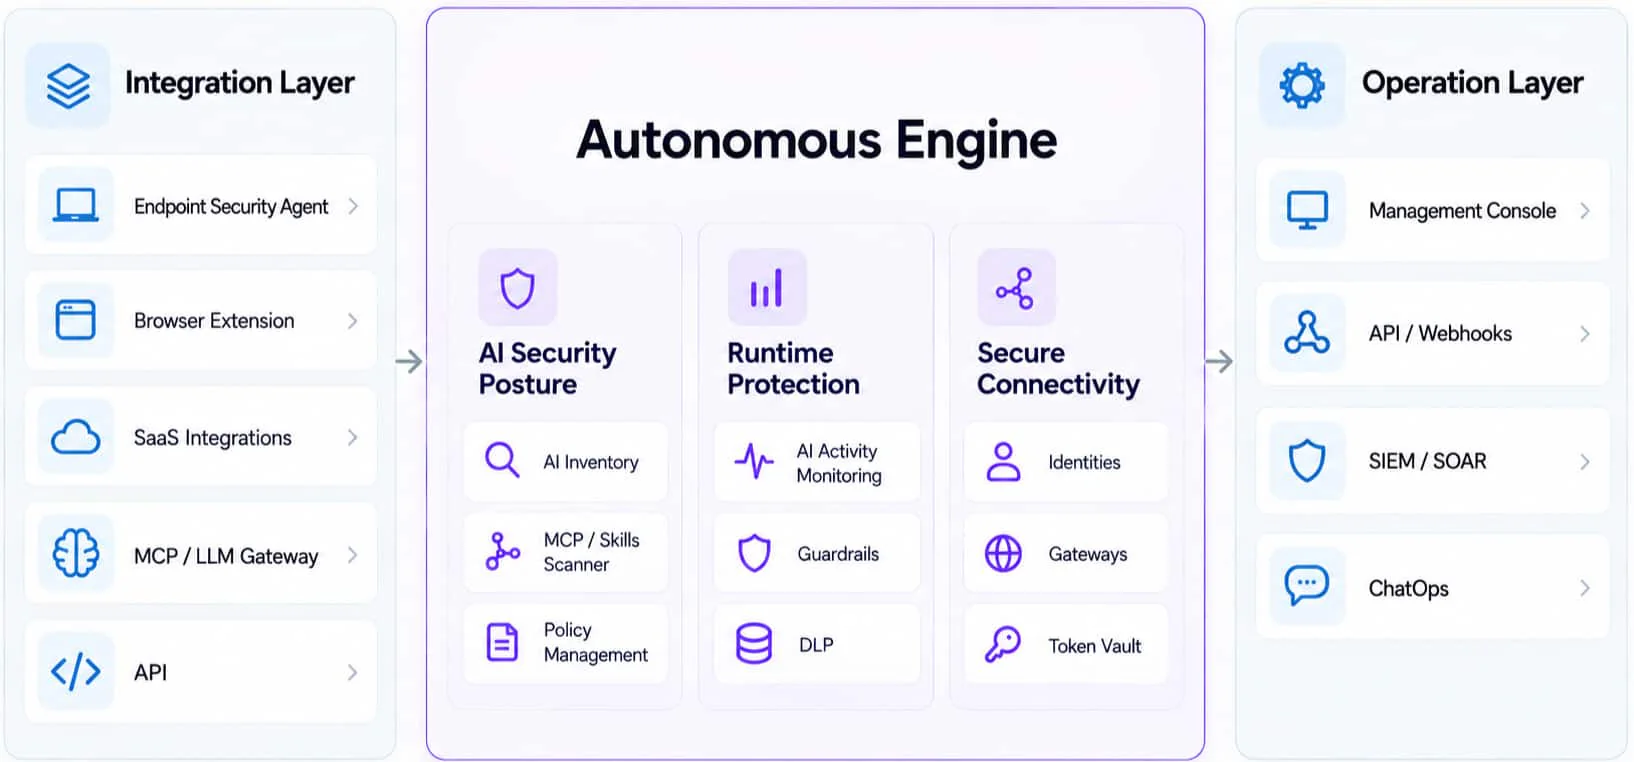
AI Security Posture
Discover Shadow AI, assess risk across MCPs, skills, and other assets, and govern what's allowed.
- AI Inventory
Discover every AI agent, application, model, account, and component in use across your organization.
- MCP / Skills Scanner
Continuously assess MCP servers and skills for vulnerabilities, malicious behavior, risky permissions, and exposed secrets.
- Policy Management
Define what is approved, restricted, or prohibited and apply those policies consistently across the organization.
Runtime Protection
Monitor agent behavior in real time, enforce AI-powered and deterministic guardrails, and keep sensitive data within approved boundaries.
- AI Activity Monitoring
See what agents are doing in real time, including prompts, tool calls, commands, data access, and actions.
- Guardrails
Fast AI-powered detection along deterministic real-time enforcement.
- DLP
Automatically restrict agentic workflows when sensitive data is accessed.
Secure Connectivity
Give agents controlled access to tools and systems with managed identities, secure gateways, and a token vault.
- Identities
Control which users and agents can access connected systems and apply access based on identity and context.
- Gateways
Secure and govern agent connections to tools, models, APIs, and MCP servers through a controlled access layer.
- Token Vault
Keep credentials out of agents by securely storing tokens and providing access without exposing the underlying secrets.
What security leaders tell us.
Thanks to Autonomous we now have full visibility into Shadow AI and our software supply chain on 4,000 endpoints.
Compared with the other platforms we tested, Autonomous got us further with far fewer ups and downs. The product depth, speed of development, and responsiveness of the team made a real difference in our decision.