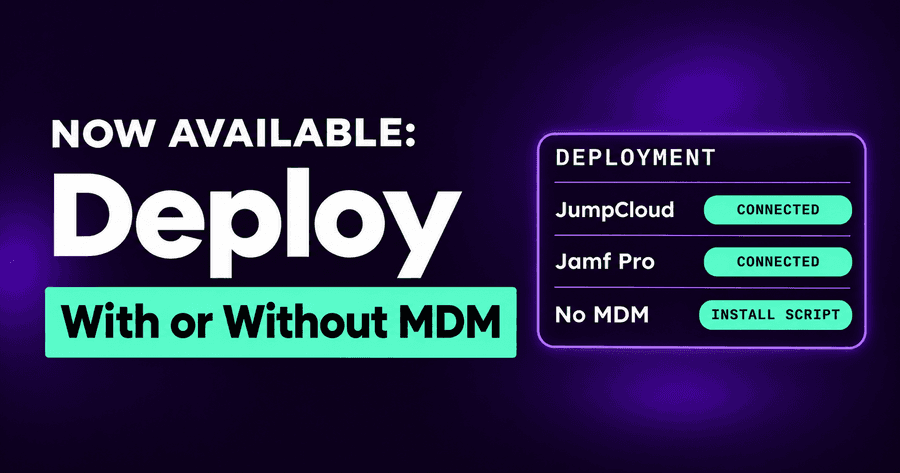
Deploy AI Agent Security with JumpCloud, Jamf Pro or No MDM
Install the AI agent security agent without an MDM, connect JumpCloud with a service account, and deploy with guides that now cover the integrations.
Insights, updates and best practices for securing AI agents, workflows and MCP.

Install the AI agent security agent without an MDM, connect JumpCloud with a service account, and deploy with guides that now cover the integrations.

Choose which models Cursor and Claude Code may use: block listed models or allow only approved ones, and block prompts from unapproved Cursor teams.

LiteLLM guardrails from Autonomous Security: mask secrets in requests, block unsafe requests, check every answer, and see each decision in Activity.

AI agent data leakage happens when a session reads sensitive data and then sends it somewhere you don't trust. Autonomous now flags or blocks that send.

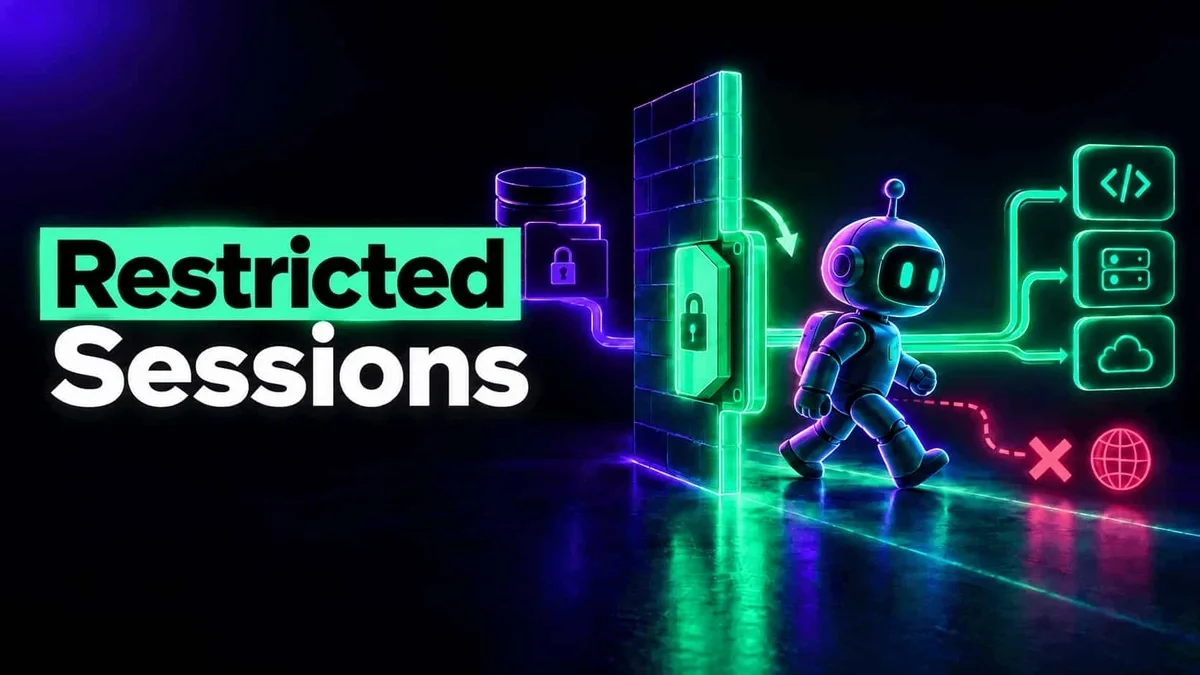
Learn how restricted sessions apply security by design to the agentic risk model, limiting data exfiltration and unsafe actions in AI agents.

Scoped API keys, a findings API and webhook in beta, and an IBM QRadar integration bring AI agent findings and audit logs into the tools your SOC already uses.

AI agents need access to sensitive systems, but they should not need the credentials behind them. This article compares common credential approaches and explains how OAuth and gateways can keep secrets outside the agent while enforcing identity, policy, and audit at the point of action.

Connect Claude Enterprise, ChatGPT Enterprise (with Codex) and Microsoft 365 Copilot and see every chat and agent session in one place, with nothing to install.

Microsoft Intune, Jamf Pro and Iru (formerly Kandji) bring your fleet and groups in, and CrowdStrike, Defender and SentinelOne show machines missing the agent.