AI Agent DLP: Email, Git, MCP and Blocked Destinations
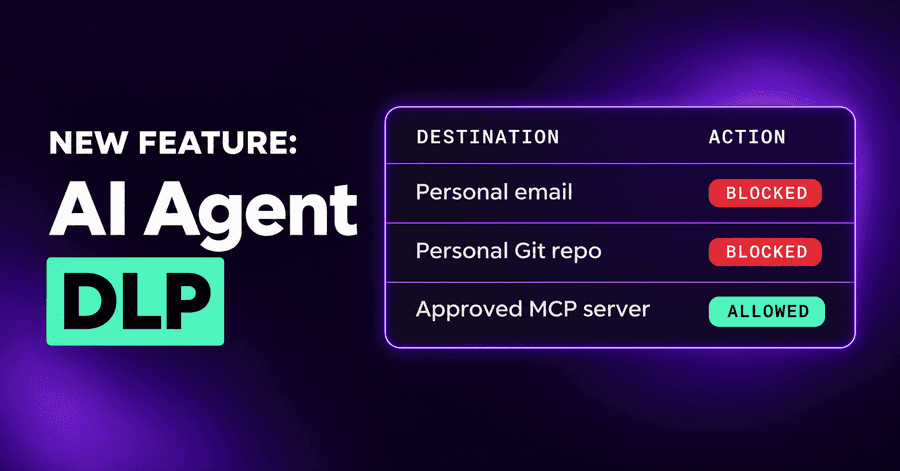
AI agent DLP now covers email, code pushed to personal repositories, MCP servers and connectors, and a list of destinations agents may never send to.
Insights, updates and best practices for securing AI agents, workflows and MCP.

AI agent DLP now covers email, code pushed to personal repositories, MCP servers and connectors, and a list of destinations agents may never send to.

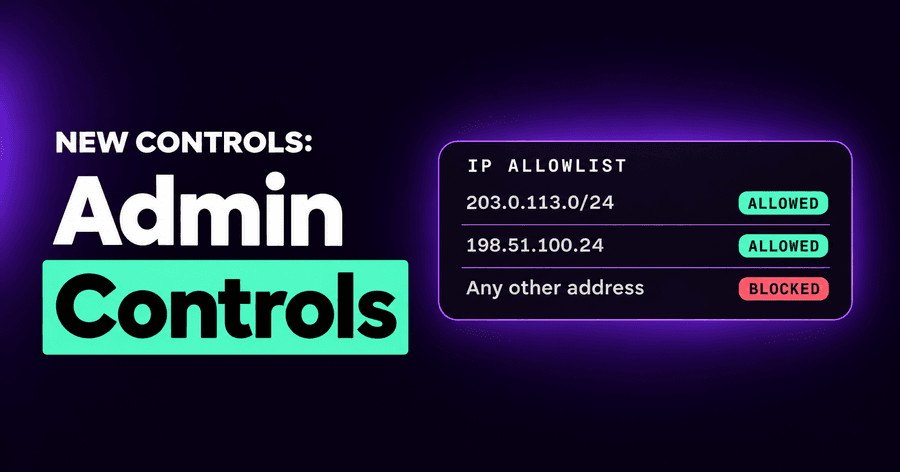
A console IP allowlist, one Enforcement tab that names the deciding rule, OWASP and MITRE tags on findings, AI spend priced per vendor, and session export.

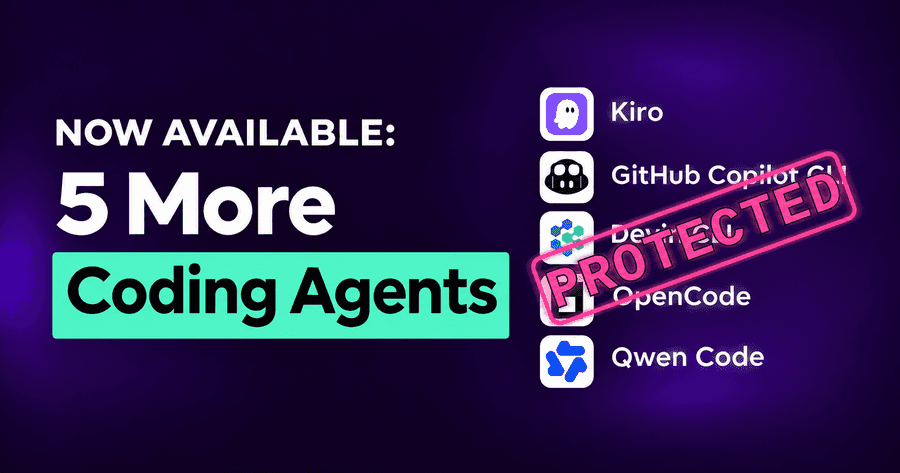
Kiro, GitHub Copilot CLI, Devin CLI, OpenCode and Qwen Code now get the same guardrails, MCP policies and inventory as the rest of your AI coding agents.

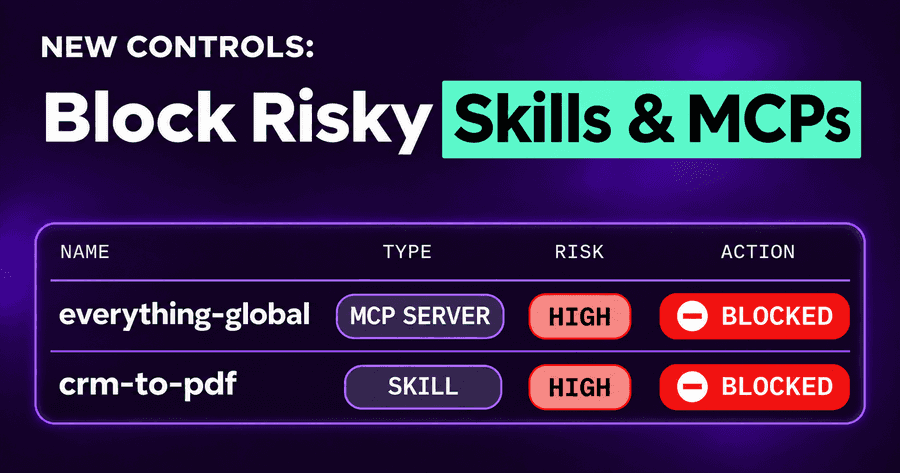
Block AI agent skills, rules and MCP servers by their risk level, pin a severity when you know better, and catch Groq, xAI, OpenRouter and Replicate keys.

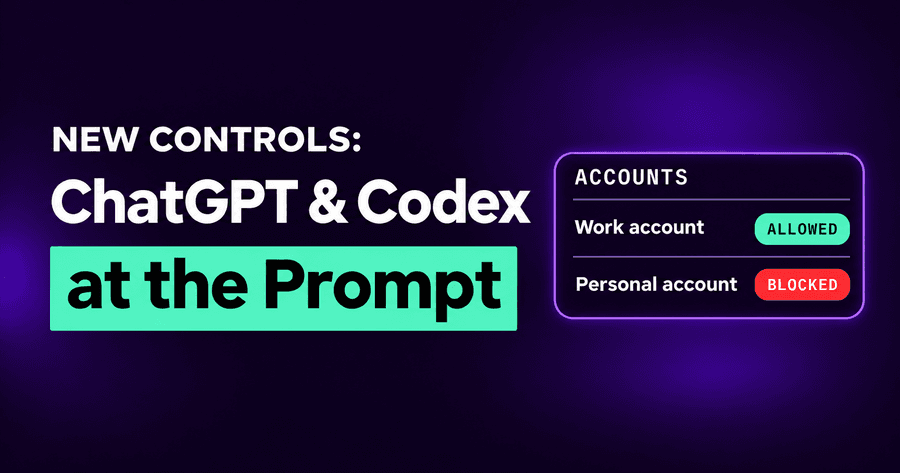
ChatGPT Desktop and Codex governed prompt by prompt: unapproved accounts and models blocked without closing the app, and apps with no controls reached too.

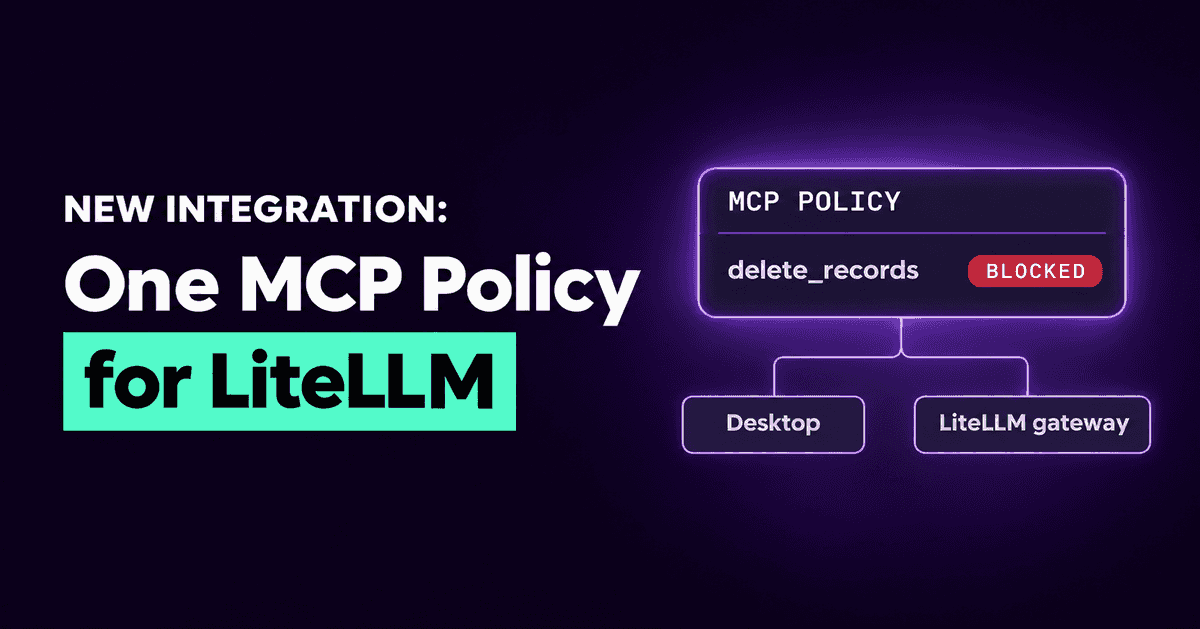
Your MCP tool rules now apply on the LiteLLM gateway too: a forbidden tool is never offered to the model, and one policy covers desktops and gateway traffic.

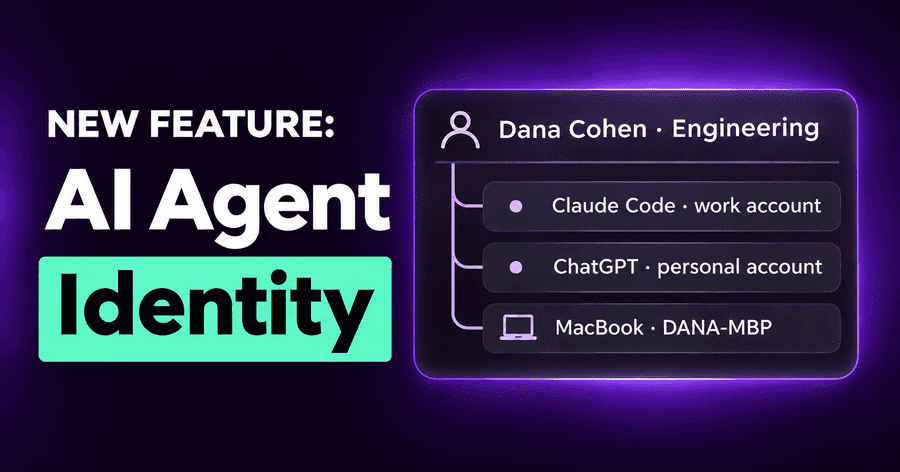
One person, many AI accounts: identity links each account and machine to the person behind it, and MCP Gateway access now follows your identity-provider groups.

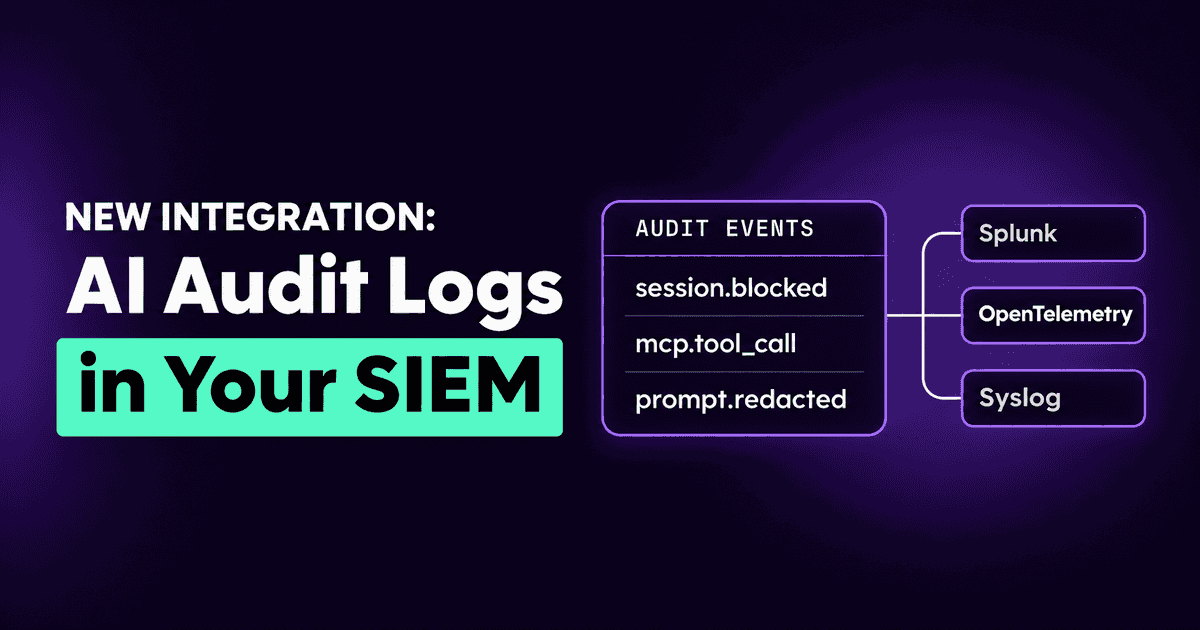
Stream the AI agent audit trail to Splunk, any OpenTelemetry collector, syslog or Coralogix, with the same event filters as Slack and webhooks.

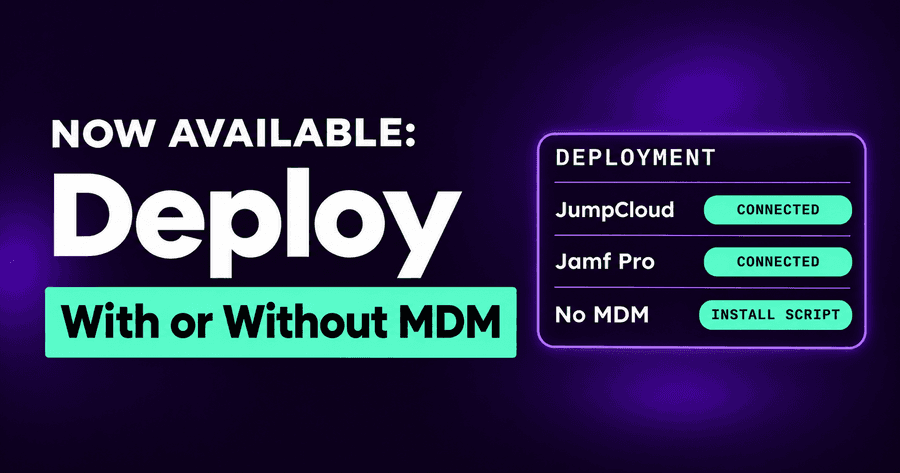
Install the AI agent security agent without an MDM, connect JumpCloud with a service account, and deploy with guides that now cover the integrations.